

[Nov 02, 2024] Get New NSE7_LED-7.0 Certification Practice Test Questions Exam Dumps
Real NSE7_LED-7.0 Exam Dumps Questions Valid NSE7_LED-7.0 Dumps PDF
Fortinet is a renowned provider of network security solutions that ensure the safety of data, devices, and networks. The company offers a range of certifications and training programs to equip IT professionals with the necessary skills to manage and secure networks. One of the certifications offered by Fortinet is the Fortinet NSE 7 - LAN Edge 7.0 or NSE7_LED-7.0 exam.
Fortinet NSE7_LED-7.0 exam is a multiple-choice, proctored exam that consists of 60 questions. NSE7_LED-7.0 exam duration is 120 minutes, and the passing score is 60%. NSE7_LED-7.0 exam can be taken online or at a Pearson VUE testing center.
NEW QUESTION # 13
Which two statements about the MAC-based 802.1X security mode available on FortiSwitch are true? (Choose two.)
- A. FortiSwitch authenticates each device connected to the port
- B. FortiSwitch authenticates a single device and opens the port to other devices connected to the port
- C. It cannot be used in conjunction with MAC authentication bypass
- D. FortiSwitch can grant different access levels to each device connected to the port
Answer: A,D
Explanation:
MAC-based 802.1X security mode allows you to authenticate each device connected to a port using its MAC address as the username and password. Therefore, Option B is true because it describes the MAC-based 802.1X security mode available on FortiSwitch. Option D is also true because FortiSwitch can grant different access levels to each device connected to the port based on the user group and security policy assigned to them.
NEW QUESTION # 14
Which two statements about MAC address quarantine by redirect mode are true? (Choose two)
- A. The quarantined device is moved to the quarantine VLAN
- B. It is the default mode for MAC address quarantine
- C. The quarantined device is kept in the current VLAN
- D. The device MACaddress is added to the Quarantined Devices firewall address group
Answer: C,D
Explanation:
Explanation
According to the FortiGate Administration Guide, "MAC address quarantine by redirect mode allows you to quarantine devices by adding their MAC addresses to a firewall address group called Quarantined Devices.
The quarantined devices are kept in their current VLANs, but their traffic is redirected to a quarantine portal." Therefore, options B and D are true because they describe the statements about MAC address quarantine by redirect mode. Option A is false because the quarantined device is not moved to the quarantine VLAN, but rather kept in the current VLAN. Option C is false because redirect mode is not the default mode for MAC address quarantine, but rather an alternative mode that can be enabled by setting mac-quarantine-mode to redirect.
https://docs.fortinet.com/document/fortiap/7.0.0/configuration-guide/734537/radius-authenticated-dynamic-vlan-: https://docs.fortinet.com/document/fortigate/7.0.0/administration-guide/734537/mac-address-quarantine
NEW QUESTION # 15
You are configuring a FortiGate wireless network to support automated wireless client quarantine using IOC. Which two configurations must you put in place for a wireless client to be quarantined successfully? (Choose two)
- A. Configure a firewall policy to allow communication
- B. Configure the wireless network to be in tunnel mode
- C. Configure the FortiGate device in the Security Fabric with a FortiAnalyzer device
- D. Configure the wireless network to be in bridge mode
Answer: B,C
NEW QUESTION # 16
Refer to the exhibit. Examine the sections of the configuration shown in the output.
What action will FortiGate take when verifying the student certificate through OCSP?
- A. Not verify the OCSP server certificate
- B. Reject the student certificate if the OCSP server replies that the student certificate status is unknown
- C. Consider the student certificate status as valid if the OCSP server is unreachable
- D. Use the OCSP URL included in the student certificate to verify the student certificate
Answer: B
Explanation:
NEW QUESTION # 17
Refer to the exhibit.
Examine the debug output shown in the exhibit
Which two statements about the RADIUS debug output are true'' (Choose two)
- A. User authentication failed
- B. The user student belongs to the SSLVPN group
- C. The RADIUS server sent a vendor-specific attribute in the RADIUS response
- D. User authentication succeeded using MSCHAP
Answer: B,D
Explanation:
Explanation
According to the exhibit, the debug output shows a RADIUS debug output from FortiGate. The output shows that FortiGate sent a RADIUS Access-Request packet to FortiAuthenticator with the username student and received a RADIUS Access-Accept packet from FortiAuthenticator with a Class attribute containing SSLVPN.
Therefore, option A is true because it indicates that the user student belongs to the SSLVPN group on FortiAuthenticator. The output also shows that FortiGate used MSCHAP as the authentication method and received a MS-MPPE-Send-Key and a MS-MPPE-Recv-Key from FortiAuthenticator. Therefore, option D is true because it indicates that user authentication succeeded using MSCHAP. Option B is false because user authentication did not fail, but rather succeeded. Option C is false because FortiAuthenticator did not send a vendor-specific attribute in the RADIUS response, but rather standard attributes defined by RFCs.
NEW QUESTION # 18
Refer to the exhibits.

Examine the firewall policy configuration and SSID settings. An administrator has configured a guest wireless network on FortiGate using the external captive portal. The administrator has verified that the external captive portal URL is correct. However wireless users are not able to see the captive portal login page. Given the configuration shown in the exhibit and the SSID settings, which configuration change should the administrator make to fix the problem?
- A. Include the wireless client subnet range in the Exempt Source section.
- B. Disable the user group from the SSID configuration.
- C. Apply a guest.portal user group in the firewall policy with the ID 11.
- D. Enable the captive-portal-exempt option in the firewall policy with the ID 11.
Answer: D
Explanation:
If using external captive portal configure policy and exempt web traffic to external captive portal.
NEW QUESTION # 19
Refer to the exhibit.
Examine the FortiGate user group configuration and the Windows AD LDAP group membership information shown in the exhibit FortiGate is configured to authenticate SSL VPN users against Windows AD using LDAP The administrator configured the SSL VPN user group for SSL VPN users However the administrator noticed that both the student and j smith users can connect to SSL VPN Which change can the administrator make on FortiGate to restrict the SSL VPN service to the student user only?
- A. In the SSL VPN user group configuration set Group Name to ::;=Domain users.CN-Users/DC=trainingAD, DC-training, DC=lab.
- B. In the SSL VPN user group configuration, change Name to cn=sslvpn, CN=users, DC=trainingAD, Detraining, DC-lab.
- C. In the SSL VPN user group configuration set Group Nam to CN-SSLVPN, CN="users, DC-trainingAD, DC-training, DC-lab
- D. In the SSL VPN user group configuration change Type to Fortinet Single Sign-On (FSSO)
Answer: C
Explanation:
Explanation
According to the FortiGate Administration Guide, "The Group Name is the name of the LDAP group that you want to use for authentication. The name must match exactly the name of the LDAP group on the LDAP server." Therefore, option A is true because it will set the Group Name to match the LDAP group that contains only the student user. Option B is false because changing the Name will not affect the authentication process, as it is only a local identifier for the user group on FortiGate. Option C is false because setting the Group Name to Domain Users will include all users in the domain, not just the student user. Option D is false because changing the Type to FSSO will require a different configuration method and will not solve the problem.
NEW QUESTION # 20
Refer to the exhibit. Examine the LDAP server configuration shown in the exhibit. Note that the Username setting has been expanded to display its full content.
On the Windows AD server 10.0.1.10, the administrator used dsquery, which returned the following output:
>dsquery user -samid student
"CN=student,CN=Users,DC=trainingAD,DC=training,DC=lab"
According to the output, which FortiGate LDAP setting is configured incorrectly?
- A. Bind Type
- B. Distinguished Name
- C. Username
- D. Common Name Identifier
Answer: B
Explanation:
According to the exhibits, the LDAP server configuration on FortiGate has the Distinguished Name set to "dc=training,dc=lab". However, according to the output of the dsquery command on the Windows AD server, the Distinguished Name of the domain should be
"dc=trainingAD,dc=training,dc=lab".
NEW QUESTION # 21
Refer to the exhibit.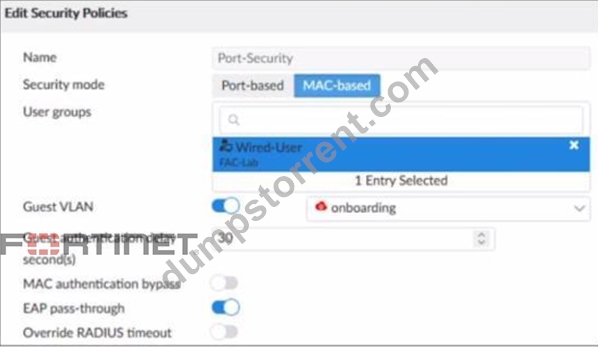
Examine the FortiSwitch security policy shown in the exhibit
If the security profile shown in the exhibit is assigned to all ports on a FortiSwitch device for 802 1X authentication which statement about the switch is correct?
- A. FortiSwitch will assign non-802 1X devices to the onboarding VLAN
- B. FortiSwitch will try to authenticate non-802 1X devices using the device MAC address as the username and password
- C. All EAP messages will be terminated on FortiSwitch
- D. FortiSwitch cannot authenticate multiple devices connected to the same port
Answer: A
Explanation:
Explanation
According to the FortiSwitch Administration Guide, "If a device does not support 802.1X authentication, you can configure the switch to assign the device to an onboarding VLAN. The onboarding VLAN is a separate VLAN that you can use to provide limited network access to non-802.1X devices." Therefore, option C is true because it describes the behavior of FortiSwitch when the security profile shown in the exhibit is assigned to all ports. Option A is false because FortiSwitch can authenticate multiple devices connected to the same port using MAC-based or MAB-EAP modes. Option B is false because FortiSwitch will not try to authenticate non-802.1X devices using the device MAC address as the username and password, but rather use MAC authentication bypass (MAB) or EAP pass-through modes. Option D is false because all EAP messages will be terminated on FortiGate, not FortiSwitch, when using 802.1X authentication.
NEW QUESTION # 22
Which CLI command should an administrator use to view the certificate verification process in real time?
- A. diagnose debug application fnbamd -1
- B. diagnose debug application foauthd -1
- C. diagnose debug application radiusd -1
- D. diagnose debug application authd -1
Answer: B
Explanation:
Explanation
According to the FortiOS CLI Reference Guide, "The diagnose debug application foauthd command enables debugging of certificate verification process in real time." Therefore, option A is true because it describes the CLI command that an administrator should use to view the certificate verification process in real time. Option B is false because diagnose debug application radiusd -1 enables debugging of RADIUS authentication process, not certificate verification process. Option C is false because diagnose debug application authd -1 enables debugging of authentication daemon process, not certificate verification process. Option D is false because diagnose debug application fnbamd -1 enables debugging of FSSO daemon process, not certificate verification process.
NEW QUESTION # 23
Which EAP method requires the use of a digital certificate on both the server end and the client end?
- A. EAP-GTC
- B. PEAP
- C. EAP-TLS
- D. EAP-TTLS
Answer: C
Explanation:
Explanation
According to the FortiGate Administration Guide, "EAP-TLS is the most secure EAP method. It requires a digital certificate on both the server end and the client end. The server and client authenticate each other using their certificates." Therefore, option D is true because it describes the EAP method that requires the use of a digital certificate on both the server end and the client end. Option A is false because EAP-TTLS only requires a digital certificate on the server end, not the client end. Option B is false because PEAP also only requires a digital certificate on the server end, not the client end. Option C is false because EAP-GTC does not require a digital certificate on either the server end or the client end.
NEW QUESTION # 24
Which EAP method requires the use of a digital certificate on both the server end and the client end?
- A. EAP-GTC
- B. PEAP
- C. EAP-TLS
- D. EAP-TTLS
Answer: C
Explanation:
EAP-TLS is the most secure EAP method. It requires a digital certificate on both the server end and the client end. The server and client authenticate each other using their certificates.
NEW QUESTION # 25
Which two pieces of information can the diagnose test authserver ldap command provide? (Choose two.)
- A. It displays whether the user credentials are correct
- B. It displays the LDAP groups found for the user
- C. It displays the LDAP codes returned by the LDAP server
- D. It displays whether the admin bind user credentials are correct
Answer: A,C
Explanation:
Explanation
According to the FortiGate CLI Reference Guide, "The diagnose test authserver ldap command tests LDAP authentication with a specific LDAP server. The command displays whether the user credentials are correct and whether the user belongs to any groups that match a firewall policy. The command also displays the LDAP codes returned by the LDAP server." Therefore, options B and C are true because they describe the information that the diagnose test authserver ldap command can provide. Option A is false because the command does not display whether the admin bind user credentials are correct, but rather whether the user credentials are correct. Option D is false because the command does not display the LDAP groups found for the user, but rather whether the user belongs to any groups that match a firewall policy.
NEW QUESTION # 26
You are setting up an SSID (VAP) to perform RADlUS-authenticated dynamic VLAN allocation Which three RADIUS attributes must be supplied by the RADIUS server to enable successful VLAN allocation'' (Choose three.)
- A. Tunnel-Private-Group-ID
- B. Tunnel-Medium-Type
- C. Tunnel-Type
- D. Tunnel-Pvt-Group-ID
- E. Tunnel-Preference
Answer: A,B,C
Explanation:
Explanation
According to the FortiAP Configuration Guide, "To perform RADIUS-authenticated dynamic VLAN allocation, the RADIUS server must supply the following RADIUS attributes: Tunnel-Private-Group-ID, which specifies the VLAN ID to assign to the user. Tunnel-Type, which specifies the tunneling protocol used for the VLAN. The value must be 13 (VLAN). Tunnel-Medium-Type, which specifies the transport medium used for the VLAN. The value must be 6 (802). Therefore, options A, D, and E are true because they describe the RADIUS attributes that must be supplied by the RADIUS server to enable successful VLAN allocation.
Option B is false because Tunnel-Pvt-Group-ID is not a valid RADIUS attribute name, but rather a typo for Tunnel-Private-Group-ID. Option C is false because Tunnel-Preference is not a required RADIUS attribute for dynamic VLAN allocation, but rather an optional attribute that specifies the priority of the VLAN.
NEW QUESTION # 27
An administrator is testing the connectivity for a new VLAN The devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate Quarantine is disabled on FortiGate While testing the administrator noticed that devices can ping FortiGate and FortiGate can ping the devices The administrator also noticed that inter-VLAN communication works However intra-VLAN communication does not work Which scenario is likely to cause this issue?
- A. Access VLAN is enabled on the VLAN
- B. The FortiGate ARP table is missing entries
- C. The native VLAN configured on the ports is incorrect
- D. The FortiSwitch MAC address table is missing entries
Answer: D
Explanation:
Explanation
According to the scenario, the devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate. Quarantine is disabled on FortiGate, which means that the devices are not blocked by any security policy. The devices can ping FortiGate and FortiGate can ping the devices, which means that the IP connectivity is working. Inter-VLAN communication works, which means that the routing between VLANs is working. However, intra-VLAN communication does not work, which means that the switching within the VLAN is not working. Therefore, option C is true because the FortiSwitch MAC address table is missing entries, which means that the FortiSwitch does not know how to forward frames to the destination MAC addresses within the VLAN. Option A is false because access VLAN is enabled on the VLAN, which means that the VLAN ID is added to the frames on ingress and removed on egress. This does not affect intra-VLAN communication. Option B is false because the native VLAN configured on the ports is incorrect, which means that the frames on the native VLAN are not tagged with a VLAN ID. This does not affect intra-VLAN communication. Option D is false because the FortiGate ARP table is missing entries, which means that FortiGate does not know how to map IP addresses to MAC addresses. This does not affect intra-VLAN communication.
NEW QUESTION # 28
Refer to the exhibit. Examine the FortiGate configuration, FortiAnalyzer logs, and FortiGate widget shown in the exhibit.
An administrator is testing the Security Fabric quarantine automation. The administrator added FortiAnalyzer to the Security Fabric, and configured an automation stitch to automatically quarantine compromised devices. The test device (10.0.2.1) is connected to a managed FortiSwitch device.
After trying to access a malicious website from the test device, the administrator verifies that FortiAnalyzer has a log for the test connection. However, the device is not getting quarantined by FortiGate, as shown in the quarantine widget.
Which two scenarios are likely to cause this issue? (Choose two.)
- A. The web filtering rating service is not working
- B. FortiAnalyzer does not consider the malicious website an indicator of compromise (IOC)
- C. The device does not have FortiClient installed
- D. FortiAnalyzer does not have a valid threat detection services license
Answer: B,D
Explanation:
According to the exhibits, the administrator has configured an automation stitch to automatically quarantine compromised devices based on FortiAnalyzer's threat detection services. However, according to the FortiAnalyzer logs, the test device is not detected as compromised by FortiAnalyzer, even though it tried to access a malicious website. Therefore, option B is true because FortiAnalyzer does not have a valid threat detection services license, which is required to enable the threat detection services feature. Option D is also true because FortiAnalyzer does not consider the malicious website an indicator of compromise (IOC), which is a criterion for identifying compromised devices.
NEW QUESTION # 29
You are configuring a FortiGate wireless network to support automated wireless client quarantine using IOC. Which two configurations must you put in place for a wireless client to be quarantined successfully? (Choose two)
- A. Configure a firewall policy to allow communication
- B. Configure the wireless network to be in tunnel mode
- C. Configure the FortiGate device in the Security Fabric with a FortiAnalyzer device
- D. Configure the wireless network to be in bridge mode
Answer: B,C
Explanation:
To enable automated wireless client quarantine using IOC, you must configure the following settings: Configure your wireless network to be in tunnel mode. This allows FortiGate to inspect all wireless traffic and apply security policies. Configure your FortiGate device in the Security Fabric with a FortiAnalyzer device. This allows FortiAnalyzer to detect indicators of compromise (IOC) from wireless traffic and send quarantine commands to FortiGate.
NEW QUESTION # 30
Which FortiSwitch VLANs are automatically created on FortiGate when the first FortiSwitch device is discovered?
- A. default quarantine, rspan voice video onboarding and nac_segment
- B. fortilink. quarantine erspan voice video and onboarding
- C. access, quarantine, rspan. voice, video, and onboarding
- D. default quarantine rspan voice video and nac_segment
Answer: A
Explanation:
NEW QUESTION # 31
When you configure a FortiAP wireless interface for auto TX power control which statement describes how it configures its transmission power?
- A. Every 30 seconds the AP will measure the signal strength of the AP using the client The AP will adjust its signal strength up or down until the AP signal is detected at -70 dBm
- B. Every 30 seconds FortiGate measures the signal strength of adjacent AP interfaces It will adjust its own AP power to match the adjacent AP signal strength
- C. Every 30 seconds FortiGate measures the signal strength of adjacent FortiAP interfaces It will adjust the adjacent AP power to be detectable at -70 dBm
- D. Every 30 seconds FortiGate measures the signal strength of the weakest associated client The AP will then configure its radio power to match the detected signal strength of the client
Answer: C
Explanation:
NEW QUESTION # 32
Refer to the exhibit.
Examine the network diagram and packet capture shown in the exhibit
The packet capture was taken between FortiGate and FortiAuthenticator and shows a RADIUS Access-Request packet sent by FortiSwitch to FortiAuthenticator through FortiGate Why does the User-Name attribute in the RADIUS Access-Request packet contain the client MAC address?
- A. FortiSwitch is authenticating the client using MAC authentication bypass
- B. The client is performing user authentication
- C. FortiSwitch is sending a RADIUS accounting message to FortiAuthenticator
- D. The client is performing AD machine authentication
Answer: A
Explanation:
Explanation
According to the exhibit, the User-Name attribute in the RADIUS Access-Request packet contains the client MAC address of 00:0c:29:6a:2b:3d. This indicates that FortiSwitch is authenticating the client using MAC authentication bypass (MAB), which is a method of authenticating devices that do not support 802.1X by using their MAC address as the username and password. Therefore, option B is true because it explains why the User-Name attribute contains the client MAC address. Option A is false because AD machine authentication uses a computer account name and password, not a MAC address. Option C is false because user authentication uses a user name and password, not a MAC address. Option D is false because FortiSwitch is sending a RADIUS Access-Request message to FortiAuthenticator, not a RADIUS accounting message.
NEW QUESTION # 33
An administrator has configured an SSID in bridge mode for corporate employees All APs are online and provisioned using default AP profiles Employees are unable to locate the SSID to conned Which two configurations can the administrator verify? (Choose two)
- A. Verify that the SSID is manually applied on AP profiles for both 2 4 GHz and 5 GHz radios
- B. Verify that the Block Intra-SSID Traffic (intra-vap-privacy) option in the SSID configuration is disabled
- C. Verify that the broadcast SSID option is enabled in the SSID configuration
- D. Verify that the SSID to an AP group that should be broadcasting the SSID is applied
Answer: C,D
Explanation:
Explanation
According to the FortiAP Configuration Guide1, "To enable the SSID, you must select at least one channel for the radio. If no channels are selected, the SSID will not be enabled. You must also enable Broadcast SSID." Therefore, option A is true because the broadcast SSID option allows the SSID to be visible to wireless clients.
Option C is also true because the SSID must be applied to an AP group that contains the APs that should be broadcasting the SSID. According to the same guide1, "You can create AP groups and assign them to different locations or departments. You can then apply different settings, such as SSIDs, to each group." Option B is false because blocking intra-SSID traffic prevents wireless clients on the same SSID from communicating with each other, which is not related to broadcasting the SSID. Option D is false because the SSID can be applied to an AP group or a global profile, which will automatically apply to all APs, without manually configuring each AP profile.
NEW QUESTION # 34
Refer to the exhibits
The exhibits show the wireless network (VAP) SSID profiles defined on FortiManager and an AP profile assigned to a group of APs that are supported by FortiGate None of the APs are broadcasting the SSlDs defined by the AP profile Which changes do you need to make to enable the SSIDs to broadcast?
- A. In the SSIDs section enable Tunnel
- B. Enable one channel in the Channels section
- C. Enable multiple channels in the Channels section and enable Radio Resource Provision
- D. In the SSIDs section enable Manual and assign the networks manually
Answer: B
Explanation:
Explanation
According to the FortiManager Administration Guide1, "To enable the SSID, you must select at least one channel for the radio. If no channels are selected, the SSID will not be enabled." Therefore, enabling one channel in the Channels section will allow the SSIDs to broadcast.
NEW QUESTION # 35
......
To earn the certification, candidates must pass a series of challenging exams that test their proficiency in these areas. Fortinet NSE 7 - LAN Edge 7.0 certification is well-regarded in the industry, as it demonstrates that the individual has both the theory and practical skills necessary to be a successful network security professional. Whether you are an experienced professional or just starting in the field, the Fortinet NSE7_LED-7.0 certification is an excellent way to showcase your expertise and advance your career.
NSE7_LED-7.0 Exam Dumps - PDF Questions and Testing Engine: https://www.dumpstorrent.com/NSE7_LED-7.0-exam-dumps-torrent.html
Latest NSE7_LED-7.0 Exam Dumps for Pass Guaranteed: https://drive.google.com/open?id=1PwhXuujqmJOHNwrvemR3JHCStaTZ_BKu