

2024 DumpsTorrent Fortinet NSE7_LED-7.0 Dumps and Exam Test Engine
Fortinet NSE7_LED-7.0 DUMPS WITH REAL EXAM QUESTIONS
Fortinet NSE7_LED-7.0 certification exam is a professional-level certification program that validates a candidate's knowledge and skills related to LAN edge security. Fortinet NSE 7 - LAN Edge 7.0 certification exam covers a wide range of topics related to Fortinet's LAN edge solutions and is intended for network security professionals with experience working with Fortinet's products. Passing the certification exam demonstrates a candidate's expertise in LAN edge security solutions and can lead to higher-paying positions in the field of network security.
NEW QUESTION # 13
Refer to the exhibit. Examine the IPsec VPN phase 1 configuration shown in the exhibit. An administrator wants to use certificate-based authentication for an IPsec VPN user.
Which three configuration changes must you make on FortiGate to perform certificate-based authentication for the IPsec VPN user? (Choose three)
- A. Import the CA that signed the user certificate
- B. Create a PKI user for the IPsec VPN user, and then configure the IPsec VPN tunnel to accept the PKI user as peer certificate
- C. In the Authentication section of the IPsec VPN tunnel in the Method drop-down list select Signature and then select the certificate that FortiGate will use for IPsec VPN
- D. Enable XAUTH on the IPsec VPN tunnel
- E. In the IKE section of the IPsec VPN tunnel in the Mode field select Main (ID protection)
Answer: A,B,C
NEW QUESTION # 14
Refer to the exhibit
Examine the FortiGate RSSO configuration shown in the exhibit
FortiGate is configured to receive RADIUS accounting messages on port3 to authenticate RSSO users The users are located behind port3 and the internet link is connected to port1 FortiGate is processing incoming RADIUS accounting messages successfully and RSSO users are getting associated with the RSSO Group user group However all the users are able to access the internet, and the administrator wants to restrict internet access to RSSO users only Which configuration change should the administrator make to fix the problem?
- A. Change the RADIUS Attribute Value selling to match the name of the RADIUS attribute containing the group membership information of the RSSO users
- B. Add RSSO Group to the firewall policy
- C. Enable Security Fabric Connection on port3
- D. Create a second firewall policy from port3 lo port1 and select the target destination subnets
Answer: B
Explanation:
Explanation
According to the exhibit, the firewall policy from port3 to port1 has no user group specified, which means that it allows all users to access the internet. Therefore, option B is true because adding RSSO Group to the firewall policy will restrict internet access to RSSO users only. Option A is false because changing the RADIUS Attribute Value setting will not affect the firewall policy, but rather the RSSO user group membership. Option C is false because enabling Security Fabric Connection on port3 will not affect the firewall policy, but rather the communication between FortiGate and other Security Fabric devices. Option D is false because creating a second firewall policy from port3 to port1 will not affect the existing firewall policy, but rather create a redundant or conflicting policy.
NEW QUESTION # 15
Refer to the exhibit
Examine the FortiGate RSSO configuration shown in the exhibit
FortiGate is configured to receive RADIUS accounting messages on port3 to authenticate RSSO users The users are located behind port3 and the internet link is connected to port1 FortiGate is processing incoming RADIUS accounting messages successfully and RSSO users are getting associated with the RSSO Group user group However all the users are able to access the internet, and the administrator wants to restrict internet access to RSSO users only Which configuration change should the administrator make to fix the problem?
- A. Change the RADIUS Attribute Value selling to match the name of the RADIUS attribute containing the group membership information of the RSSO users
- B. Add RSSO Group to the firewall policy
- C. Enable Security Fabric Connection on port3
- D. Create a second firewall policy from port3 lo port1 and select the target destination subnets
Answer: B
Explanation:
Explanation
According to the exhibit, the firewall policy from port3 to port1 has no user group specified, which means that it allows all users to access the internet. Therefore, option B is true because adding RSSO Group to the firewall policy will restrict internet access to RSSO users only. Option A is false because changing the RADIUS Attribute Value setting will not affect the firewall policy, but rather the RSSO user group membership. Option C is false because enabling Security Fabric Connection on port3 will not affect the firewall policy, but rather the communication between FortiGate and other Security Fabric devices. Option D is false because creating a second firewall policy from port3 to port1 will not affect the existing firewall policy, but rather create a redundant or conflicting policy.
NEW QUESTION # 16
Refer to the exhibit.
Examine the debug output shown in the exhibit
Which two statements about the RADIUS debug output are true'' (Choose two)
- A. User authentication failed
- B. The user student belongs to the SSLVPN group
- C. The RADIUS server sent a vendor-specific attribute in the RADIUS response
- D. User authentication succeeded using MSCHAP
Answer: B,D
Explanation:
Explanation
According to the exhibit, the debug output shows a RADIUS debug output from FortiGate. The output shows that FortiGate sent a RADIUS Access-Request packet to FortiAuthenticator with the username student and received a RADIUS Access-Accept packet from FortiAuthenticator with a Class attribute containing SSLVPN.
Therefore, option A is true because it indicates that the user student belongs to the SSLVPN group on FortiAuthenticator. The output also shows that FortiGate used MSCHAP as the authentication method and received a MS-MPPE-Send-Key and a MS-MPPE-Recv-Key from FortiAuthenticator. Therefore, option D is true because it indicates that user authentication succeeded using MSCHAP. Option B is false because user authentication did not fail, but rather succeeded. Option C is false because FortiAuthenticator did not send a vendor-specific attribute in the RADIUS response, but rather standard attributes defined by RFCs.
NEW QUESTION # 17
When you configure a FortiAP wireless interface for auto TX power control which statement describes how it configures its transmission power?
- A. Every 30 seconds the AP will measure the signal strength of the AP using the client The AP will adjust its signal strength up or down until the AP signal is detected at -70 dBm
- B. Every 30 seconds FortiGate measures the signal strength of adjacent AP interfaces It will adjust its own AP power to match the adjacent AP signal strength
- C. Every 30 seconds FortiGate measures the signal strength of adjacent FortiAP interfaces It will adjust the adjacent AP power to be detectable at -70 dBm
- D. Every 30 seconds FortiGate measures the signal strength of the weakest associated client The AP will then configure its radio power to match the detected signal strength of the client
Answer: C
Explanation:
NEW QUESTION # 18
Refer to the exhibits. Examine the troubleshooting outputs shown in the exhibits.
Users have been reporting issues with the speed of their wireless connection in a particular part of the wireless network. The interface that is having issues is the 2.4 GHz interface that is currently configured on channel 6.
The administrator of the wireless network has investigated and surveyed the local RF environment using the tools available at the AP and FortiGate.
Which configuration would improve the wireless connection?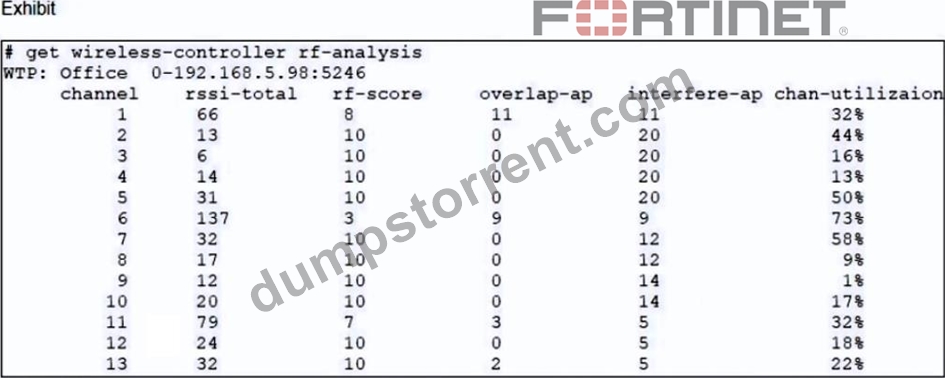

- A. Change the AP 2.4 GHz channel to 13.
- B. Change the AP 2.4 GHz channel to 9.
- C. Change the AP 2.4 GHz channel to 11
- D. Change the AP 2.4 GHz channel to 1.
Answer: D
Explanation:
According to the exhibits, the AP 2.4 GHz interface is currently configured on channel 6, which is overlapping with other nearby APs on channels 4 and 8. This can cause interference and reduce the wireless performance. Therefore, changing the AP 2.4 GHz channel to 1 would improve the wireless connection, as it would avoid the overlapping channels and use a non-overlapping channel instead.
NEW QUESTION # 19
Which EAP method requires the use of a digital certificate on both the server end and the client end?
- A. EAP-GTC
- B. PEAP
- C. EAP-TLS
- D. EAP-TTLS
Answer: C
Explanation:
Explanation
According to the FortiGate Administration Guide, "EAP-TLS is the most secure EAP method. It requires a digital certificate on both the server end and the client end. The server and client authenticate each other using their certificates." Therefore, option D is true because it describes the EAP method that requires the use of a digital certificate on both the server end and the client end. Option A is false because EAP-TTLS only requires a digital certificate on the server end, not the client end. Option B is false because PEAP also only requires a digital certificate on the server end, not the client end. Option C is false because EAP-GTC does not require a digital certificate on either the server end or the client end.
NEW QUESTION # 20
Where can FortiGate learn the FortiManager IP address or FQDN for zero-touch provisioning'?
- A. From a TFTP server
- B. From a DNS server using A or AAAA records
- C. From an LDAP server using a simple bind operation
- D. From a DHCP server using options 240 and 241
Answer: D
Explanation:
FG retrieves the FortiManager IP address or FQDN through DHCP options 240 or 241 respectively.
NEW QUESTION # 21
An administrator has configured an SSID in bridge mode for corporate employees All APs are online and provisioned using default AP profiles Employees are unable to locate the SSID to conned Which two configurations can the administrator verify? (Choose two)
- A. Verify that the SSID is manually applied on AP profiles for both 2 4 GHz and 5 GHz radios
- B. Verify that the Block Intra-SSID Traffic (intra-vap-privacy) option in the SSID configuration is disabled
- C. Verify that the broadcast SSID option is enabled in the SSID configuration
- D. Verify that the SSID to an AP group that should be broadcasting the SSID is applied
Answer: C,D
Explanation:
Explanation
According to the FortiAP Configuration Guide1, "To enable the SSID, you must select at least one channel for the radio. If no channels are selected, the SSID will not be enabled. You must also enable Broadcast SSID." Therefore, option A is true because the broadcast SSID option allows the SSID to be visible to wireless clients.
Option C is also true because the SSID must be applied to an AP group that contains the APs that should be broadcasting the SSID. According to the same guide1, "You can create AP groups and assign them to different locations or departments. You can then apply different settings, such as SSIDs, to each group." Option B is false because blocking intra-SSID traffic prevents wireless clients on the same SSID from communicating with each other, which is not related to broadcasting the SSID. Option D is false because the SSID can be applied to an AP group or a global profile, which will automatically apply to all APs, without manually configuring each AP profile.
NEW QUESTION # 22
Refer to the exhibits.

Examine the firewall policy configuration and SSID settings. An administrator has configured a guest wireless network on FortiGate using the external captive portal. The administrator has verified that the external captive portal URL is correct. However wireless users are not able to see the captive portal login page. Given the configuration shown in the exhibit and the SSID settings, which configuration change should the administrator make to fix the problem?
- A. Include the wireless client subnet range in the Exempt Source section.
- B. Disable the user group from the SSID configuration.
- C. Apply a guest.portal user group in the firewall policy with the ID 11.
- D. Enable the captive-portal-exempt option in the firewall policy with the ID 11.
Answer: D
Explanation:
If using external captive portal configure policy and exempt web traffic to external captive portal.
NEW QUESTION # 23
Refer to the exhibit. In the wireless configuration shown in the exhibits, an AP is deployed in a remote site and has a wireless network (VAP) called Corporate deployed to it. The network is a tunneled network however clients connecting to a wireless network require access to a local printer. Clients are trying to print to a printer on the remote site but are unable to do so.
Which configuration change is required to allow clients connected to the Corporate SSID to print locally?

- A. Configure split-tunneling in the wtp-profile configuration
- B. Disable the Block Intra-SSID Traffic (intra-vap-privacy) setting on the SSID (VAP) profile
- C. Configure split-tunneling in the vap configuration
- D. Configure the printer as a wireless client on the Corporate wireless network
Answer: C
Explanation:
Split tunneling allows you to specify which traffic is tunneled to the FortiGate and which traffic is sent directly to the Internet. This can improve performance and reduce bandwidth usage.
Therefore, by configuring split-tunneling in the vap configuration, you can allow the clients connected to the Corporate SSID to access both the corporate network and the local printer.
NEW QUESTION # 24
Refer to the exhibit.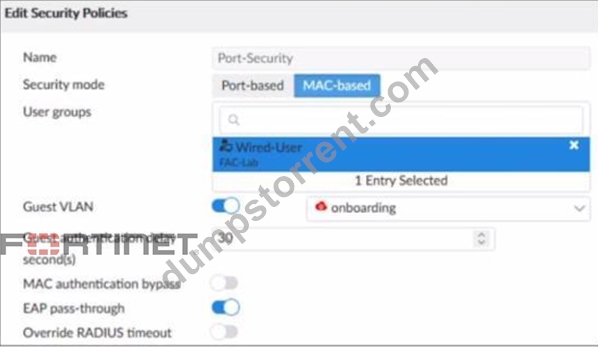
Examine the FortiSwitch security policy shown in the exhibit
If the security profile shown in the exhibit is assigned to all ports on a FortiSwitch device for 802 1X authentication which statement about the switch is correct?
- A. FortiSwitch will assign non-802 1X devices to the onboarding VLAN
- B. FortiSwitch will try to authenticate non-802 1X devices using the device MAC address as the username and password
- C. All EAP messages will be terminated on FortiSwitch
- D. FortiSwitch cannot authenticate multiple devices connected to the same port
Answer: A
Explanation:
Explanation
According to the FortiSwitch Administration Guide, "If a device does not support 802.1X authentication, you can configure the switch to assign the device to an onboarding VLAN. The onboarding VLAN is a separate VLAN that you can use to provide limited network access to non-802.1X devices." Therefore, option C is true because it describes the behavior of FortiSwitch when the security profile shown in the exhibit is assigned to all ports. Option A is false because FortiSwitch can authenticate multiple devices connected to the same port using MAC-based or MAB-EAP modes. Option B is false because FortiSwitch will not try to authenticate non-802.1X devices using the device MAC address as the username and password, but rather use MAC authentication bypass (MAB) or EAP pass-through modes. Option D is false because all EAP messages will be terminated on FortiGate, not FortiSwitch, when using 802.1X authentication.
NEW QUESTION # 25
Refer to the exhibit. Examine the FortiSwitch security policy shown in the exhibit. If the security profile shown in the exhibit is assigned to all ports on a FortiSwitch device for 802.1X authentication, which statement about the switch is correct?
- A. FortiSwitch will assign non-802.1X devices to the onboarding VLAN
- B. All EAP messages will be terminated on FortiSwitch
- C. FortiSwitch will try to authenticate non-802.1X devices using the device MAC address as the username and password
- D. FortiSwitch cannot authenticate multiple devices connected to the same port
Answer: A
Explanation:
In cases where y device does not support 802.1x you can configure the security profile to place that device in the VLAN selected as GuestVLAN.
NEW QUESTION # 26 
Wireless guest users are unable to authenticate because they are getting a certificate error while loading the captive portal login page.This URL string is the HTTPS POST URL guest wireless users see when attempting to access the network using the web browser
Which two settings are the likely causes of the issue? (Choose two.)
- A. The user address is not in DDNS form
- B. The wireless user's browser is missing a CA certificate
- C. The FortiGate authentication interface address is using HTTPS
- D. The external server FQDN is incorrect
Answer: B,D
Explanation:
Explanation
According to the exhibit, the wireless guest users are getting a certificate error while loading the captive portal login page. This means that the browser cannot verify the identity of the server that is hosting the login page.
Therefore, option A is true because the external server FQDN is incorrect, which means that it does not match the common name or subject alternative name of the server certificate. Option B is also true because the wireless user's browser is missing a CA certificate, which means that it does not have the root or intermediate certificate that issued the server certificate. Option C is false because the FortiGate authentication interface address is using HTTPS, which is a secure protocol that encrypts the communication between the browser and the server. Option D is false because the user address is not in DDNS form, which is not related to the certificate error.
NEW QUESTION # 27
Refer to the exhibit. Examine the FortiGate user group configuration and the Windows AD LDAP group membership information shown in the exhibit.
FortiGate is configured to authenticate SSL VPN users against Windows AD using LDAP. The administrator configured the SSL VPN user group for SSL VPN users. However the administrator noticed that both the student and j.smith users can connect to SSL VPN.
Which change can the administrator make on FortiGate to restrict the SSL VPN service to the student user only?
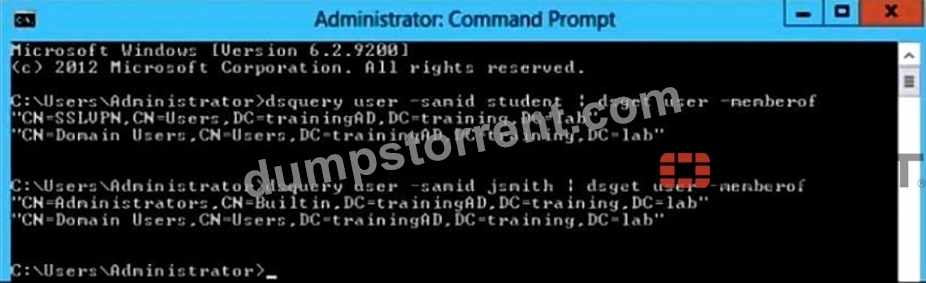
- A. In the SSL VPN user group configuration, change Type to Fortinet Single Sign-On (FSSO).
- B. In the SSL VPN user group configuration, change Name to
CN=SSLVPN,CN=Users,DC=trainingAD,DC=training,DC=lab. - C. In the SSL VPN user group configuration, set Group Name to
CN=SSLVPN,CN=Users,DC=trainingAD,DC=training,DC=lab. - D. In the SSL VPN user group configuration, set Group Name to CN=Domain Users,CN=Users,DC=trainingAD,DC=training,DC=lab.
Answer: C
Explanation:
The Group Name is the name of the LDAP group that you want to use for authentication. The name must match exactly the name of the LDAP group on the LDAP server.
NEW QUESTION # 28
Which two pieces of information can the diagnose test authserver ldap command provide? (Choose two.)
- A. It displays whether the user credentials are correct
- B. It displays the LDAP groups found for the user
- C. It displays the LDAP codes returned by the LDAP server
- D. It displays whether the admin bind user credentials are correct
Answer: A,C
Explanation:
Explanation
According to the FortiGate CLI Reference Guide, "The diagnose test authserver ldap command tests LDAP authentication with a specific LDAP server. The command displays whether the user credentials are correct and whether the user belongs to any groups that match a firewall policy. The command also displays the LDAP codes returned by the LDAP server." Therefore, options B and C are true because they describe the information that the diagnose test authserver ldap command can provide. Option A is false because the command does not display whether the admin bind user credentials are correct, but rather whether the user credentials are correct. Option D is false because the command does not display the LDAP groups found for the user, but rather whether the user belongs to any groups that match a firewall policy.
NEW QUESTION # 29
Refer to the exhibit. Examine the network diagram and packet capture shown in the exhibit.
The packet capture was taken between FortiGate and FortiAuthenticator, and shows a RADIUS Access-Request packet sent by FortiSwitch to FortiAuthenticator through FortiGate.
Why does the User-Name attribute in the RADIUS Access-Request packet contain the client MAC address?
- A. FortiSwitch is authenticating the client using MAC authentication bypass
- B. The client is performing user authentication
- C. FortiSwitch is sending a RADIUS accounting message to FortiAuthenticator
- D. The client is performing AD machine authentication
Answer: A
Explanation:
According to the exhibit, the User-Name attribute in the RADIUS Access-Request packet contains the client MAC address of 00:0c:29:6a:2b:3d. This indicates that FortiSwitch is authenticating the client using MAC authentication bypass (MAB), which is a method of authenticating devices that do not support 802.1X by using their MAC address as the username and password.
NEW QUESTION # 30
Where can FortiGate learn the FortiManager IP address or FQDN for zero-touch provisioning'?
- A. From a DHCP server using options 240 and 241
- B. From a TFTP server
- C. From a DNS server using A or AAAA records
- D. From an LDAP server using a simple bind operation
Answer: C
Explanation:
Explanation
According to the FortiGate Administration Guide, "FortiGate can learn the FortiManager IP address or FQDN for zero-touch provisioning from a DNS server using A or AAAA records. The DNS server must be configured to resolve the hostname fortimanager.fortinet.com to the IP address or FQDN of the FortiManager device." Therefore, option D is true because it describes the method for FortiGate to learn the FortiManager IP address or FQDN for zero-touch provisioning. Option A is false because LDAP is not used for zero-touch provisioning. Option B is false because TFTP is not used for zero-touch provisioning. Option C is false because DHCP options 240 and 241 are not used for zero-touch provisioning.
NEW QUESTION # 31
Refer to the exhibits.
Firewall Policy
Examine the firewall policy configuration and SSID settings
An administrator has configured a guest wireless network on FortiGate using the external captive portal The administrator has verified that the external captive portal URL is correct However wireless users are not able to see the captive portal login page Given the configuration shown in the exhibit and the SSID settings which configuration change should the administrator make to fix the problem?
- A. Apply a guest.portal user group in the firewall policy with the ID 11.
- B. Disable the user group from the SSID configuration
- C. Enable the captivs-portal-exempt option in the firewall policy with the ID 11.
- D. Include the wireless client subnet range in the Exempt Source section
Answer: A
Explanation:
Explanation
According to the FortiGate Administration Guide, "To use an external captive portal, you must configure a user group that uses the external captive portal as the authentication method and apply it to a firewall policy." Therefore, option C is true because it will allow the wireless users to be redirected to the external captive portal URL when they try to access the Internet. Option A is false because disabling the user group from the SSID configuration will prevent the wireless users from being authenticated by the FortiGate device. Option B is false because enabling the captive-portal-exempt option in the firewall policy will bypass the captive portal authentication for the wireless users, which is not the desired outcome. Option D is false because including the wireless client subnet range in the Exempt Source section will also bypass the captive portal authentication for the wireless users, which is not the desired outcome.
NEW QUESTION # 32
Which CLI command should an administrator use to view the certificate verification process in real time?
- A. diagnose debug application fnbamd -1
- B. diagnose debug application foauthd -1
- C. diagnose debug application radiusd -1
- D. diagnose debug application authd -1
Answer: B
Explanation:
Explanation
According to the FortiOS CLI Reference Guide, "The diagnose debug application foauthd command enables debugging of certificate verification process in real time." Therefore, option A is true because it describes the CLI command that an administrator should use to view the certificate verification process in real time. Option B is false because diagnose debug application radiusd -1 enables debugging of RADIUS authentication process, not certificate verification process. Option C is false because diagnose debug application authd -1 enables debugging of authentication daemon process, not certificate verification process. Option D is false because diagnose debug application fnbamd -1 enables debugging of FSSO daemon process, not certificate verification process.
NEW QUESTION # 33
Refer to the exhibit showing certificate values.
Wireless guest users are unable to authenticate because they are getting a certificate error while loading the captive portal login page. This URL string is the HTTPS POST URL guest wireless users see when attempting to access the network using the web browser:
https://fac.trainingad.training.com/guests/login/?
login&post=https://auth.trainingad.training.lab:1003/fgtauth&magic=000a038293d1f411&usermac
=b8:27:eb:d8:50:02&apmac=70:4c:a5:9d:0d:28&apip=10.10.100.2&userip=10.0.3.1&ssid=Guest0
3&apname=PS221ETF18000148&bssid=70:4c:a5:9d:0d:30
Which two settings are the likely causes of the issue? (Choose two.)
- A. The user address is not in DDNS form
- B. The wireless user's browser is missing a CA certificate
- C. The FortiGate authentication interface address is using HTTPS
- D. The external server FQDN is incorrect
Answer: B,D
Explanation:
According to the exhibit, the wireless guest users are getting a certificate error while loading the captive portal login page. This means that the browser cannot verify the identity of the server that is hosting the login page. Therefore, option A is true because the external server FQDN is incorrect, which means that it does not match the common name or subject alternative name of the server certificate. Option B is also true because the wireless user's browser is missing a CA certificate, which means that it does not have the root or intermediate certificate that issued the server certificate.
NEW QUESTION # 34
An administrator is testing the connectivity for a new VLAN The devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate Quarantine is disabled on FortiGate While testing the administrator noticed that devices can ping FortiGate and FortiGate can ping the devices The administrator also noticed that inter-VLAN communication works However intra-VLAN communication does not work Which scenario is likely to cause this issue?
- A. Access VLAN is enabled on the VLAN
- B. The FortiGate ARP table is missing entries
- C. The native VLAN configured on the ports is incorrect
- D. The FortiSwitch MAC address table is missing entries
Answer: D
Explanation:
Explanation
According to the scenario, the devices in the VLAN are connected to a FortiSwitch device that is managed by FortiGate. Quarantine is disabled on FortiGate, which means that the devices are not blocked by any security policy. The devices can ping FortiGate and FortiGate can ping the devices, which means that the IP connectivity is working. Inter-VLAN communication works, which means that the routing between VLANs is working. However, intra-VLAN communication does not work, which means that the switching within the VLAN is not working. Therefore, option C is true because the FortiSwitch MAC address table is missing entries, which means that the FortiSwitch does not know how to forward frames to the destination MAC addresses within the VLAN. Option A is false because access VLAN is enabled on the VLAN, which means that the VLAN ID is added to the frames on ingress and removed on egress. This does not affect intra-VLAN communication. Option B is false because the native VLAN configured on the ports is incorrect, which means that the frames on the native VLAN are not tagged with a VLAN ID. This does not affect intra-VLAN communication. Option D is false because the FortiGate ARP table is missing entries, which means that FortiGate does not know how to map IP addresses to MAC addresses. This does not affect intra-VLAN communication.
NEW QUESTION # 35
Refer to the exhibits
The exhibits show the wireless network (VAP) SSID profiles defined on FortiManager and an AP profile assigned to a group of APs that are supported by FortiGate None of the APs are broadcasting the SSlDs defined by the AP profile Which changes do you need to make to enable the SSIDs to broadcast?
- A. In the SSIDs section enable Tunnel
- B. Enable one channel in the Channels section
- C. Enable multiple channels in the Channels section and enable Radio Resource Provision
- D. In the SSIDs section enable Manual and assign the networks manually
Answer: B
Explanation:
Explanation
According to the FortiManager Administration Guide1, "To enable the SSID, you must select at least one channel for the radio. If no channels are selected, the SSID will not be enabled." Therefore, enabling one channel in the Channels section will allow the SSIDs to broadcast.
NEW QUESTION # 36
Refer to the exhibit.
Examine the FortiGate user group configuration and the Windows AD LDAP group membership information shown in the exhibit FortiGate is configured to authenticate SSL VPN users against Windows AD using LDAP The administrator configured the SSL VPN user group for SSL VPN users However the administrator noticed that both the student and j smith users can connect to SSL VPN Which change can the administrator make on FortiGate to restrict the SSL VPN service to the student user only?
- A. In the SSL VPN user group configuration set Group Name to ::;=Domain users.CN-Users/DC=trainingAD, DC-training, DC=lab.
- B. In the SSL VPN user group configuration, change Name to cn=sslvpn, CN=users, DC=trainingAD, Detraining, DC-lab.
- C. In the SSL VPN user group configuration set Group Nam to CN-SSLVPN, CN="users, DC-trainingAD, DC-training, DC-lab
- D. In the SSL VPN user group configuration change Type to Fortinet Single Sign-On (FSSO)
Answer: C
Explanation:
Explanation
According to the FortiGate Administration Guide, "The Group Name is the name of the LDAP group that you want to use for authentication. The name must match exactly the name of the LDAP group on the LDAP server." Therefore, option A is true because it will set the Group Name to match the LDAP group that contains only the student user. Option B is false because changing the Name will not affect the authentication process, as it is only a local identifier for the user group on FortiGate. Option C is false because setting the Group Name to Domain Users will include all users in the domain, not just the student user. Option D is false because changing the Type to FSSO will require a different configuration method and will not solve the problem.
NEW QUESTION # 37
......
Fortinet is a leading provider of enterprise network security solutions and has developed the NSE7_LED-7.0 exam to test the capabilities of professionals who work with their products. Fortinet NSE 7 - LAN Edge 7.0 certification validates an individual's expertise in configuring and managing Fortinet products such as FortiGate, FortiSwitch, and FortiAP. Earning the Fortinet NSE 7 - LAN Edge 7.0 certification demonstrates a candidate's commitment to their profession and their ability to protect their organization's LAN edge infrastructure from cyber threats.
Fortinet NSE7_LED-7.0 is an examination offered by Fortinet that validates the knowledge and skills of professionals who work with Fortinet NSE 7 - LAN Edge 7.0 solutions. It is designed to test the understanding of concepts, principles, and practices related to Fortinet NSE 7 - LAN Edge 7.0.
2024 New DumpsTorrent NSE7_LED-7.0 PDF Recently Updated Questions: https://www.dumpstorrent.com/NSE7_LED-7.0-exam-dumps-torrent.html
NSE7_LED-7.0 Exam with Guarantee Updated 38 Questions: https://drive.google.com/open?id=1_fy6D0s8iHQKXJPGKU_K80KGrsFJ_jZV