

PCNSE Exam Dumps - PDF Questions and Testing Engine
PCNSE Dumps - The Sure Way To Pass Exam
What is the duration of the PCNSE Exam
- Number of Questions: 75
- Format: Multiple choices, multiple answers
- Length of Examination: 80 minutes
Sample Questions
Which configuration must be made on the firewall before it can read User-ID-to-IP-address mapping tables from external sources?
- D. User-ID Agents
- B. Server Monitoring
- C. Captive Portal
- A. Group Mapping Settings
For an external device to consume a local User-ID-to-IP-address mapping table, which data is used for authentication between the devices?
- D. certificates added to the User-ID agent configuration
- A. the source device's Data Redistribution Collector Name and Pre-Shared Key
- C. administrators account information on the source device with the User-ID role set
- B. User-ID agent's Server Monitor Account information
User-ID-to IP-address mapping tables can be read by which product or service?
- C. AutoFocus
- B. Panorama Log Collector
- A. Cortex XDR
- D. Prisma Cloud
Certification Overview
The Palo Alto Networks Certified Network Security Engineer is an advanced-level certification. This formal certificate validates that one possesses in-depth knowledge of the Palo Alto Networks product portfolio and can deploy it in a vast number of implementations. Commonly, the Palo Alto Networks product portfolio comprises multiple separate technologies working in unison to ward off cyber attacks. To a security-conscious employer, being PCNSE-certified provides additional assurance of one’s ability to correctly deploy the Palo Alto Networks Next-Generation Firewalls and manage the Palo Alto Networks technology. The Palo Alto Network’s reputation as a high-end security provider makes their validations highly valued by many organizations. This is why all of their certifications are considered prestigious. Are you wondering what the earnings potential and opportunities for IT specialists with the PCNSE certification look like? Well, PCNSE-certified IT professionals can expect to earn around $94,000 annually, according to Payscale.
NEW QUESTION 64
The manager of the network security team has asked you to help configure the company's Security Profiles according to Palo Alto Networks best practice As part of that effort, the manager has assigned you the Vulnerability Protection profile for the internet gateway firewall Which action and packet-capture setting for items of high severity and critical severity best matches Palo Alto Networks best practice'?
- A. action 'default' and packet capture 'single-packet'
- B. action 'reset-both' and packet capture 'extended-capture'
- C. action 'reset-both' and packet capture 'single-packet'
- D. action 'reset-server' and packet capture 'disable'
Answer: D
NEW QUESTION 65
Which four NGFW multi-factor authentication factors are supported by PAN-OS? (Choose four.)
- A. User logon
- B. Short message service
- C. SSH key
- D. One-Time Password
- E. Voice
- F. Push
Answer: B,D,E,F
Explanation:
https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-admin/authentication/authentication-types/multi-factor-authentication
Push - An endpoint device (such as a phone or tablet) prompts the user to allow or deny authentication.
Short message service (SMS) - An SMS message on the endpoint device prompts the user to allow or deny authentication. In some cases, the endpoint device provides a code that the user must enter in the MFA login page.
Voice - An automated phone call prompts the user to authenticate by pressing a key on the phone or entering a code in the MFA login page.
One-time password (OTP) - An endpoint device provides an automatically generated alphanumeric string, which the user enters in the MFA login page to enable authentication for a single transaction or session.
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/authentication/authentication-types/multi-factor-authentication.html#idbc927952-a47e-4bec-ab80-0605a47b4873
NEW QUESTION 66
Which three items are import considerations during SD-WAN configuration planning? (Choose three.)
- A. link requirements
- B. IP Addresses
- C. branch and hub locations
- D. the name of the ISP
Answer: A,B,C
NEW QUESTION 67
A remote administrator needs access to the firewall on an untrust interlace. Which three options would you configure on an interface Management profile lo secure management access? (Choose three)
- A. Permitted IP Addresses
- B. SSH
- C. HTTPS
- D. User-ID
- E. HTTP
Answer: A,B,C
NEW QUESTION 68
Click the Exhibit button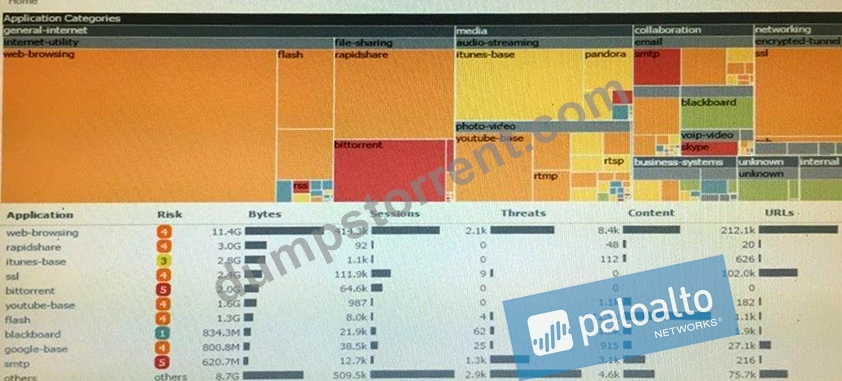
An administrator has noticed a large increase in bittorrent activity. The administrator wants to determine where the traffic is going on the company.
What would be the administrator's next step?
- A. Right-Click on the bittorrent link and select Value from the context menu
- B. Create a global filter for bittorrent traffic and then view Traffic logs.
- C. Click on the bittorrent application link to view network activity
- D. Create local filter for bittorrent traffic and then view Traffic logs.
Answer: C
NEW QUESTION 69
Exhibit: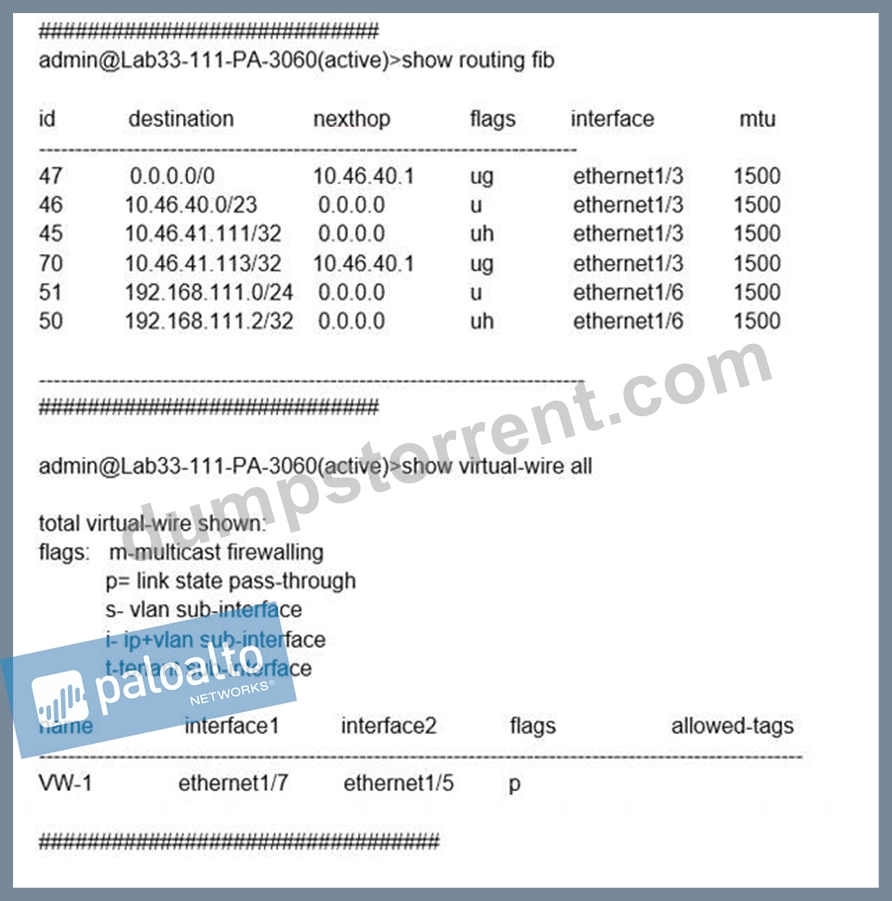
What will be the egress interface if the traffic's ingress interface is ethernet1/6 sourcing from 192.168.111.3 and to the destination 10.46.41.113 during the time shown in the image?
- A. ethernet1/6
- B. ethernet1/5
- C. ethernet1/7
- D. ethernet1/3
Answer: D
NEW QUESTION 70
An administrator has been asked to create 100 virtual firewalls in a local, on-premise lab environment (not in "the cloud"). Bootstrapping is the most expedient way to perform this task.
Which option describes deployment of a bootstrap package in an on-premise virtual environment?
- A. Use a virtual CD-ROM with an ISO.
- B. Create and attach a virtual hard disk (VHD).
- C. Use an S3 bucket with an ISO.
- D. Use config-drive on a USB stick.
Answer: A
Explanation:
Explanation/Reference:
Reference: https://www.paloaltonetworks.com/documentation/80/virtualization/virtualization/set-up-the-vm- series-firewall-on-kvm/install-the-vm-series-firewall-on-kvm/use-an-iso-file-to-deploy-the-vm-series-firewall
NEW QUESTION 71
A firewall should be advertising the static route 10 2 0 0/24 into OSPF The configuration on the neighbor is correct but the route is not in the neighbor's routing table Which two configurations should you check on the firewall'? (Choose two )
- A. Ensure that the OSPF neighbor state is "2-Way"
- B. Within the redistribution profile ensure that Redist is selected
- C. In the OSFP configuration ensure that the correct redistribution profile is selected in the OSPF Export Rules section
- D. In the redistribution profile check that the source type is set to "ospf"
Answer: B,C
NEW QUESTION 72
Refer to the exhibit.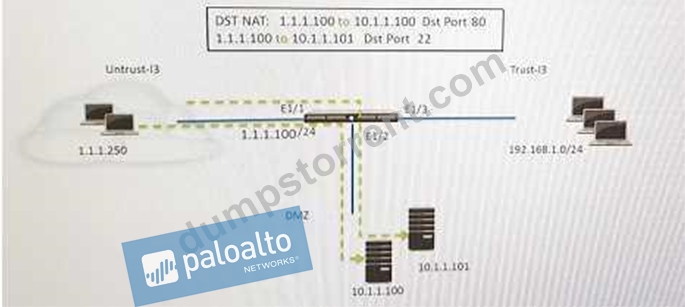
An administrator is using DNAT to map two servers to a single public IP address. Traffic will be steered to the specific server based on the application, where Host A (10.1.1.100) receives HTTP traffic and HOST B (10.1.1.101) receives SSH traffic.) Which two security policy rules will accomplish this configuration? (Choose two.)
- A. Untrust (Any) to Untrust (10.1.1.1), ssh -Allow
- B. Untrust (Any) to DMZ (10.1.1.1), ssh -Allow
- C. Untrust (Any) to Untrust (10.1.1.1), web-browsing -Allow
- D. Untrust (Any) to DMZ (10.1.1.1), web-browsing -Allow
- E. Untrust (Any) to DMZ (10.1.1.100.10.1.1.101), ssh, web-browsing -Allow
Answer: B,D
NEW QUESTION 73
A company needs to preconfigure firewalls to be sent to remote sites with the least amount of reconfiguration. Once deployed, each firewall must establish secure tunnels back to multiple regional data centers to include the future regional data centers.
Which VPN configuration would adapt to changes when deployed to the future site?
- A. Preconfigured GlobalProtect client
- B. Preconfigured PPTP Tunnels
- C. Preconfigured GlobalProtect satellite
- D. Preconfigured IPsec tunnels
Answer: C
Explanation:
https://docs.paloaltonetworks.com/pan-os/10-0/pan-os-admin/large-scale-vpn-lsvpn/configure-the-globalprotect-portal-for-lsvpn/define-the-satellite-configurations.html
NEW QUESTION 74
Which Panorama feature allows for logs generated by Panorama to be forwarded to an external Security Information and Event Management(SIEM) system?
- A. Panorama Device Group Log Forwarding
- B. Panorama Log Settings
- C. Panorama Log Templates
- D. Collector Log Forwarding for Collector Groups
Answer: B
Explanation:
https://www.paloaltonetworks.com/documentation/61/panorama/panorama_admiHYPERLINK
"https://www.paloaltonetworks.com/documentation/61/panorama/panorama_adminguide/manag e-log-collection/enable-log-forwarding-from-panorama-to-external-destinations"nguidHYPERLINK
"https://www.paloaltonetworks.com/documentation/61/panorama/panorama_adminguide/manag e-log-collection/enable-log-forwarding-from-panorama-to-external-destinations"e/manage-log- collection/enable-log-forwarding-from-panorama-to-external-destinaHYPERLINK
"https://www.paloaltonetworks.com/documentation/61/panorama/panorama_adminguide/manag e-log-collection/enable-log-forwarding-from-panorama-to-external-destinations"tions
NEW QUESTION 75
A client wants to detect the use of weak and manufacturer-default passwords for loT devices. Which option will help the customer?
- A. Configure an Antivirus profile with alert mode.
- B. Configure a Data Filtering profile with alert mode.
- C. Configure a Vulnerability Protection profile with alert mode
- D. Configure an Anti-Spyware profile with alert mode.
Answer: C
NEW QUESTION 76
A firewall administrator requires an A/P HA pair to fail over more quickly due to critical business application uptime requirements.
What is the correct setting?
- A. Change the HA timer profile to "user-defined" and manually set the timers.
- B. Change the HA timer profile to "quick" and customize in advanced profile.
- C. Change the HA timer profile to "fast".
- D. Change the HA timer profile to "aggressive" or customize the settings in advanced profile.
Answer: D
Explanation:
Use the Recommended profile for typical failover timer settings and the Aggressive profile for faster failover timer settings. The Advanced profile allows you to customize the timer values to suit your network requirements.
Reference: https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/high-availability/set-up- activepassive-ha/configure-activepassive-ha.html
NEW QUESTION 77
An administrator needs to determine why users on the trust zone cannot reach certain websites. The only information available is shown on the following image. Which configuration change should the administrator make?
A: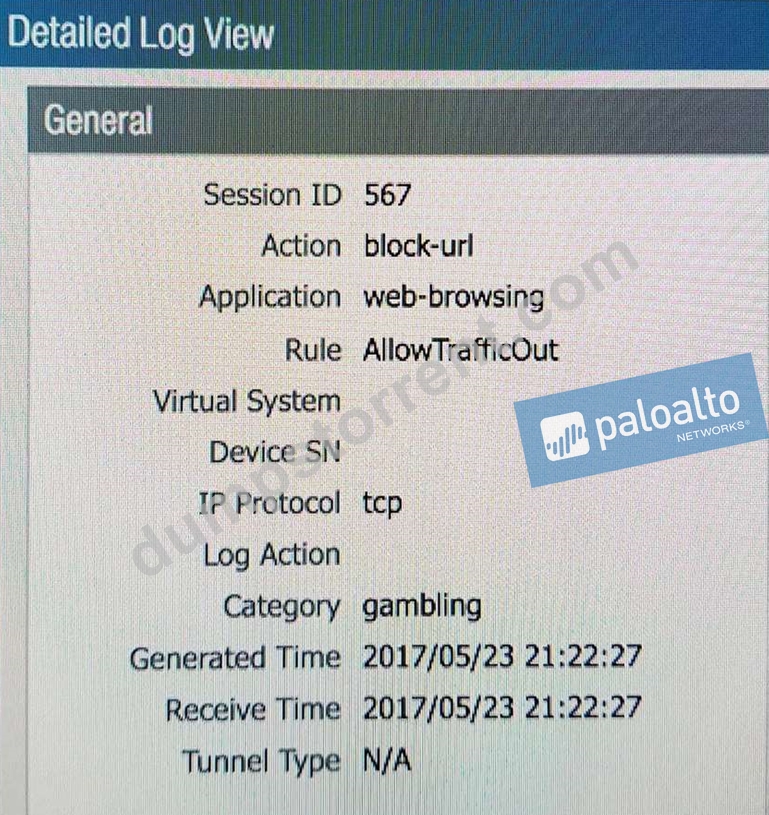
B: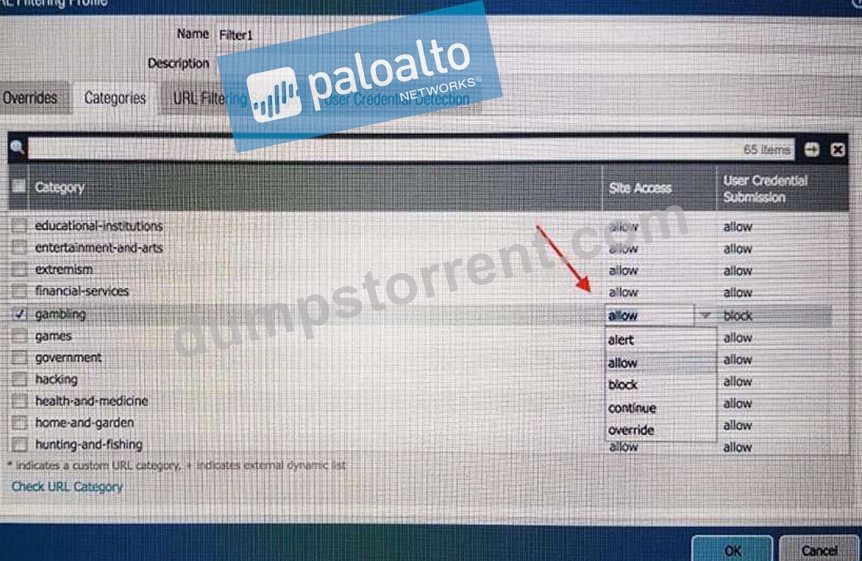
C: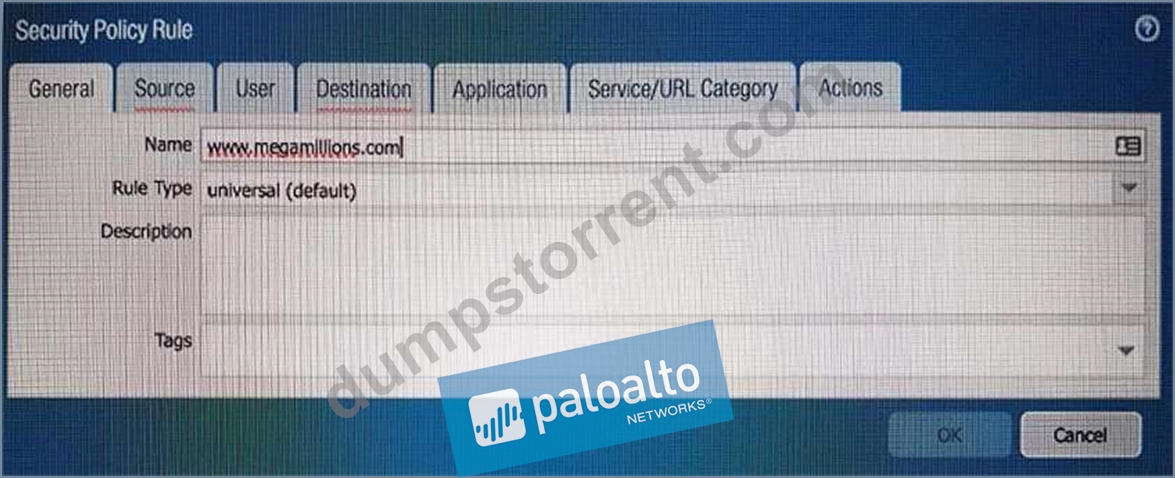
D: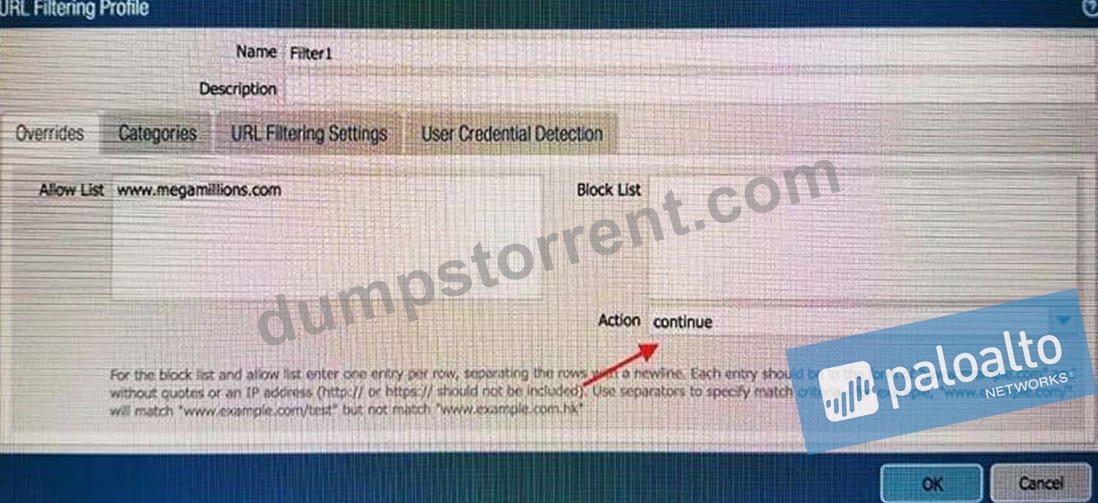
E: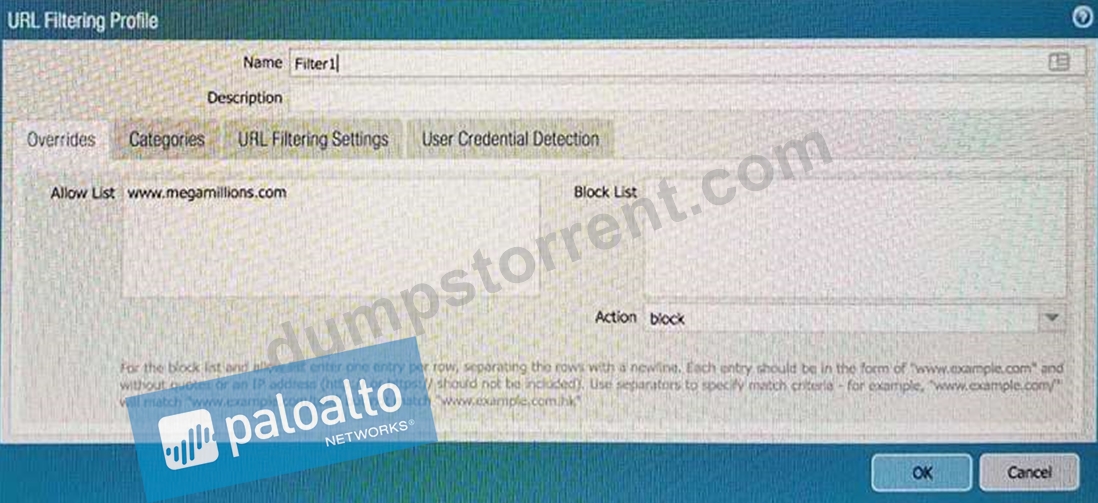
- A. Option A
- B. Option D
- C. Option B
- D. Option E
- E. Option C
Answer: C
NEW QUESTION 78
Which administrative authentication method supports authorization by an external service?
- A. Certificates
- B. RADIUS
- C. LDAP
- D. SSH keys
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/firewall-administration/manage-firewall-administrators/administrative-authentication
NEW QUESTION 79
Panorama provides which two SD_WAN functions? (Choose two.)
- A. physical network links
- B. data plane
- C. control plane
- D. network monitoring
Answer: C,D
NEW QUESTION 80
An administrator needs to upgrade an NGFW to the most current version of PAN-OS?software.
The following is occurring:
- Firewall has internet connectivity through e 1/1.
- Default security rules and security rules allowing all SSL and web-
browsing traffic to and from any zone.
- Service route is configured, sourcing update traffic from e1/1.
- A communication error appears in the System logs when updates are
performed.
- Download does not complete.
What must be configured to enable the firewall to download the current version of PAN-OS software?
- A. Security policy rule allowing PaloAlto-updates as the application
- B. Static route pointing application PaloAlto-updates to the update servers
- C. Scheduler for timed downloads of PAN-OS software
- D. DNS settings for the firewall to use for resolution
Answer: D
NEW QUESTION 81
......
Pass Palo Alto Networks PCNSE Exam Quickly With DumpsTorrent: https://www.dumpstorrent.com/PCNSE-exam-dumps-torrent.html
PCNSE Exam Questions (Updated 2022) 100% Real Question Answers: https://drive.google.com/open?id=1alNtEHqp9Akyx2sOjqa5tfaOW-iVjNPV